DNSMadeEasy started off as quite a good platform until it was bought by DigiCert recently. The following article represents our own findings and own observations based on raw data. Readers should reach their own conclusions based on what is presented.
We have noticed a constant increase in the DNS lookup of a lot of their domains managed by DNSMadeEasy in the last couple of years. This certainly happened with a couple of the clients that we manage DNS records for and we have well over 200 domain names now; we had more before we started moving away to another supplier because we noticed the steady and unexplained DNS look up over the past couple of years.
There is a tool called DNS Analytics (offered by DNSMadeEasy) that used to allow you to download the RAW data for queries which included the IP addresses that queried your domain names. It looks like DNSMadeEasy may have since switched this function off.
We have noticed that every month we are being billed for extra DNS queries that we never had before; even though we have been moving our high traffic domain names away from them. We are only left with some low traffic domain names yet every month the queries still go over the allocated threshold.
When we analyse the raw queries we notice a number of glaring issues. (1) We are being billed for IPv6 traffic and we don’t use IPv6 at all for any of our domain names nor on any of our infrastructure yet there is no way to switch this off.
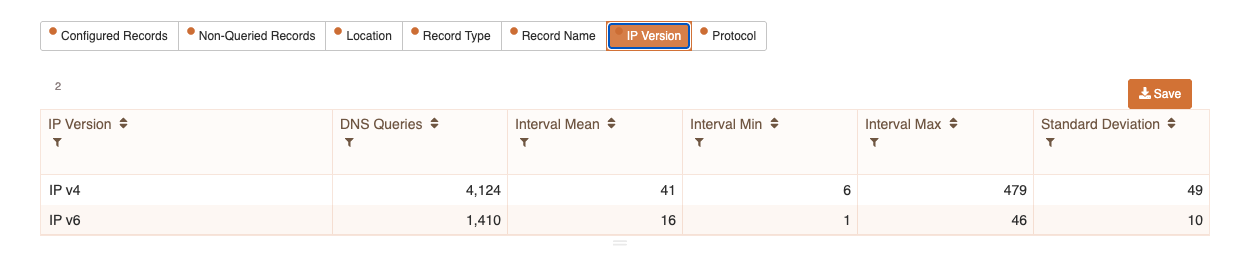
In fact we don’t even support IPv6 in any of our infrastructure nor had we set any IPv6 looks up on any of the domain names; yet we are being charged every month for the look ups and moreover there is no way to block these queries.
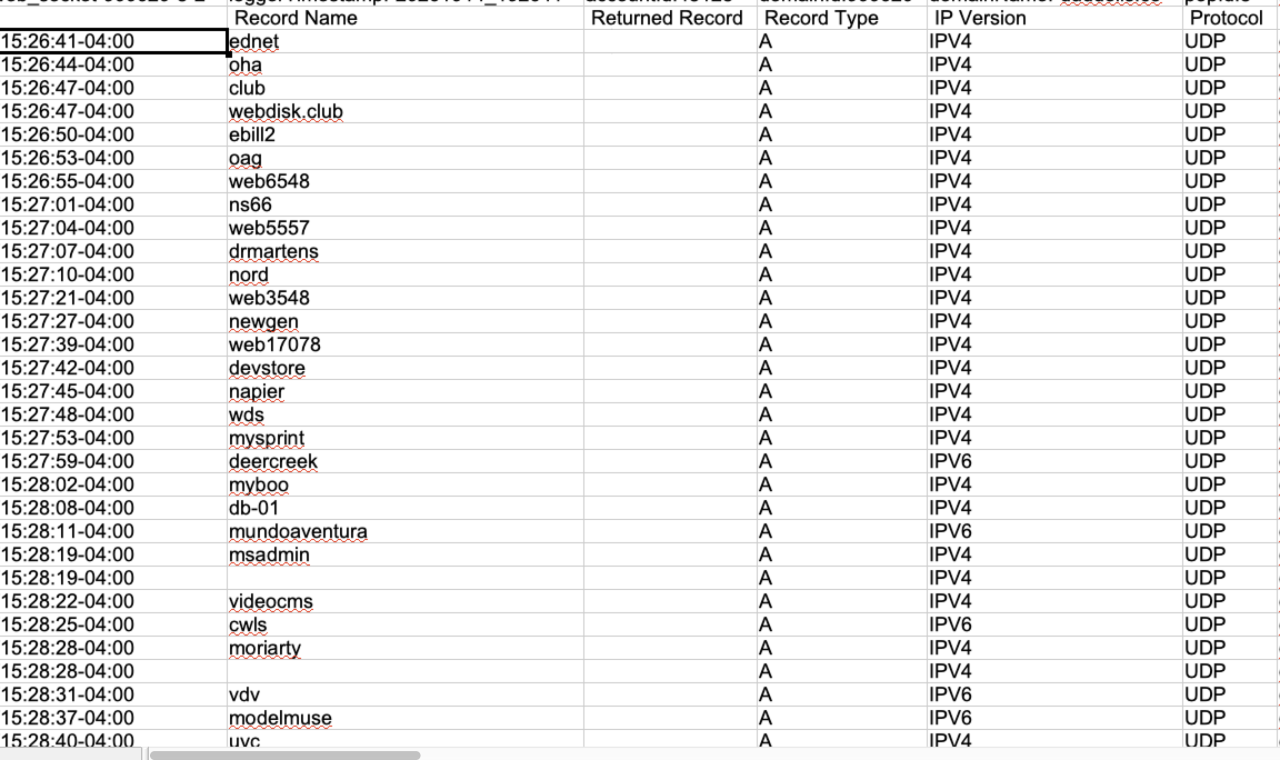
(2) We noticed a huge number of lookups from Frankfurt and New York every month. We can see that these look ups are all spam and we even suspect could well be created by DNS Made Easy or their affiliates so that they can charge us extra. The below is part of a raw log of lookups – 95% of the records do not even exist and use the UDP protocol; in fact we can probably switch of UDP altogether as hardly any of our services use UDP. So we are being charged for lookups that don’t exist and there is no way to block them and nor does DNSMadeEasy have any intention of creating a function for to block them.
Our clients are predominantly based in Asia and many of them have very little interaction with clients in Europe or the USA; yet from the raw data it looks like most of the traffic is coming from Frankfurt and America.
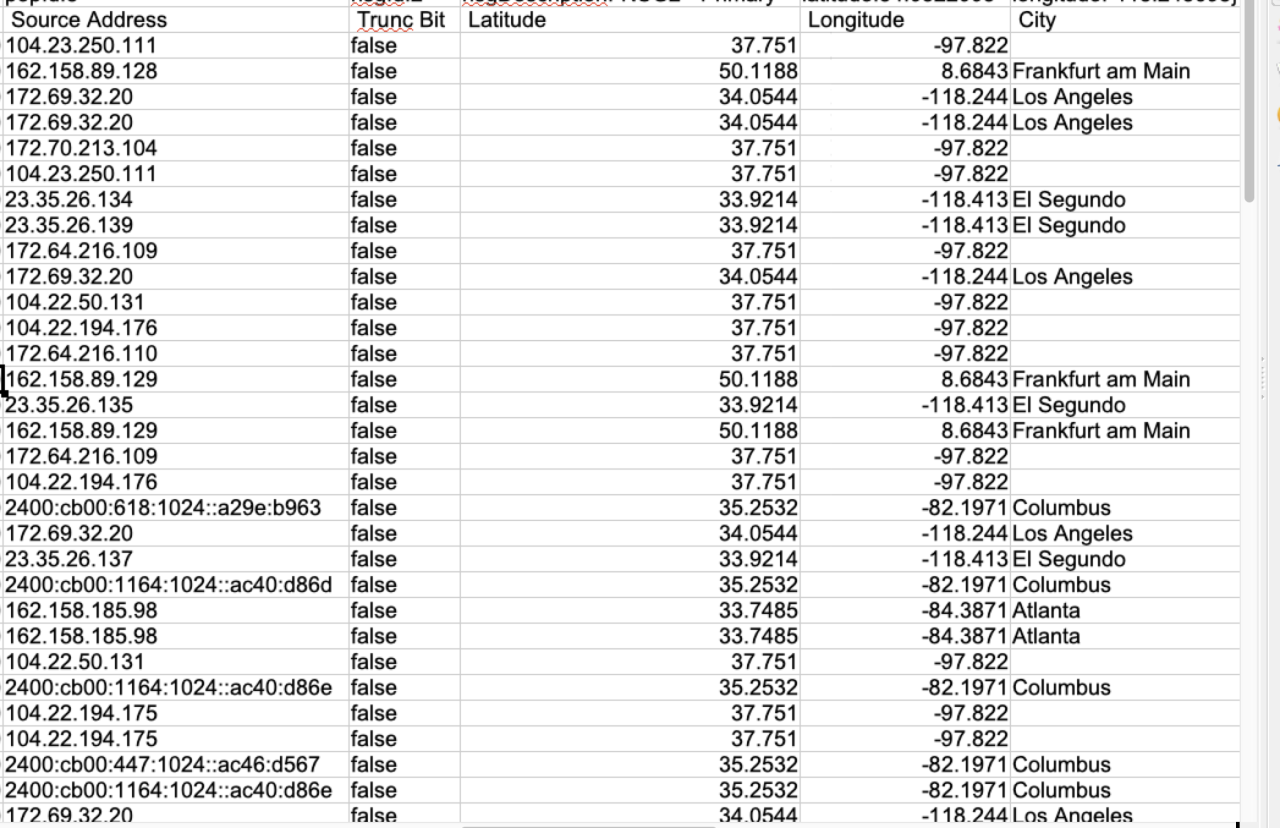
It seems that the IP address block from “Frankfurt” 162.158.89.128 e.g. 162.158.89.0/24 is creating a lot of the lookup traffic. But when I do a look up of the IP Address on IPinfo.info – it shows that these IP addresses belong to CloudFlare:-
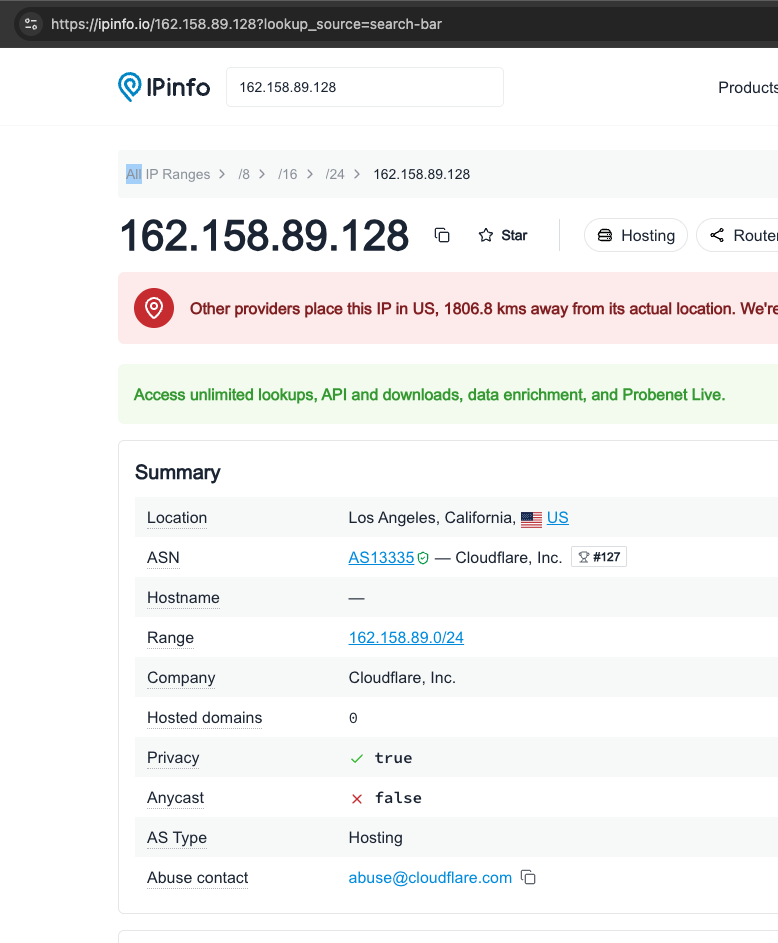
What is strange is that the IP address (162.158.89.128) that DNSMadeEasy has designated as being from Frankfurt is shown to belong to CloudFlare (A competitor of DNSMadeEasy) on IPInfo. We did a look up for the IP address 172.69.32.20 and yet again it looks like it belongs to CloudFlare:-
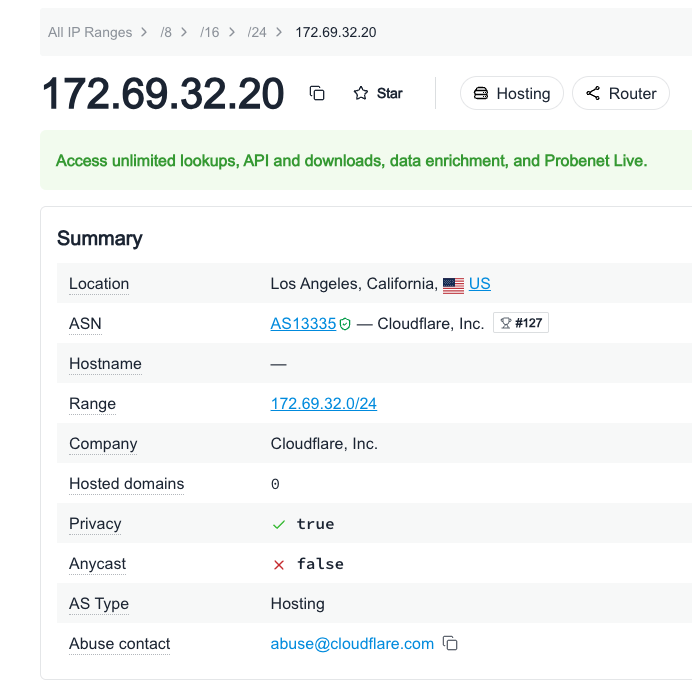
So is CloudFlare deliberately making these queries for DNSMadeEasy hosted domains to try to get users to move across to them or is DNSMadeEasy a willing victim since it’s getting them more revenue?